Blog
Exactly-Once Log Summaries with Sentinel data lake and Fabric - Part 1: The Idea
Summarization and Current Limitations Firewall, DNS and proxy logs produce millions of events a day. Keeping them all in the Sentinel analytics tier is expensive; keeping them only in the data lake means no analytics …
Auditing Sentinel Queries with Decision Models
Who Read What? SOC analysts run hundreds of KQL queries against Microsoft Sentinel every day, and the data they read is anything but harmless: passwords leaked into command lines, email subjects, sometimes card numbers …
Sentinel Data Lake 2.0
On 23 September 2026, Microsoft changed how new customers get the Microsoft Sentinel data lake experience. Most posts since then focus on the simpler onboarding, but the update also changes which features you get and how …
Sentinel Protected Tables
Microsoft Sentinel workspaces tend to hold tables that were never meant for a wide audience - HR investigation logs, insider threat cases, AI prompt histories, sign-in records full of PII - or security data in general. …
A Prompt Is Not a Lock: Read-Only Modes in AI Harnesses
After an incident with Claude Code in which my code was overwritten while I was in Plan Mode - a mode whose premise is that it does not touch the code - I decided to dig deeper into how AI harnesses actually work, and …
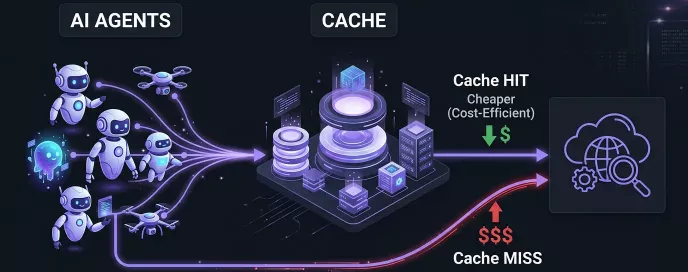
Prompt Caching for Semi-Autonomous SOC Agents with Anthropic
Building AI-enhanced SOC tooling is now pretty straightforward, and plenty of companies are rolling their own. What started as chatbot assistants has grown into semi-autonomous (or sometimes fully autonomous) agents that …
Patching the Sentinel MCP server for safety
MCP servers are now the default way to connect AI to real systems, tools and data. In SOC scenarios, they are used to pull logs, run hunts, and automate response steps. It feels clean and simple: you ask the model, it …
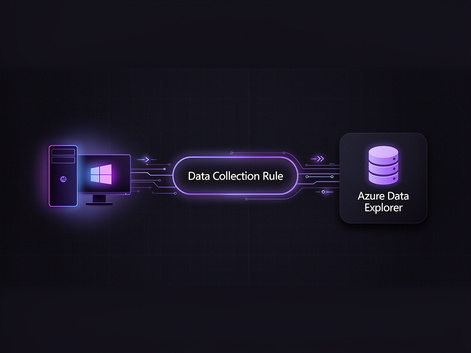
Logs to ADX from all your machines via AMA
In a previous post, I explored how Azure Monitor Agent (AMA) could turn Event Hubs into a reliable, scalable backbone for your logging infrastructure, effortlessly pulling logs from Azure VMs and routing them to Event …